 CakesCats PBAsedutil
Hardware disk encryption. Free.
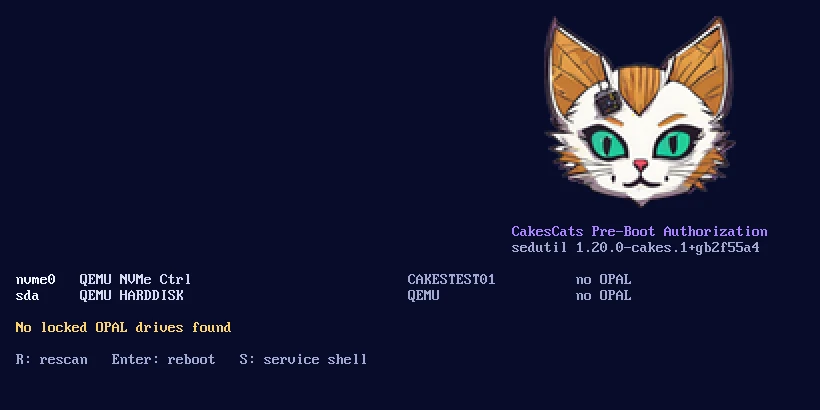
CakesCats PBA is a maintained fork of sedutil for self-encrypting SSDs. It asks for the password before the OS starts, unlocks the drive and boots on. Corporate suites sell exactly this per seat; here it is open source and free. For companies, we customise it, with SSO and MDM.
Overview
Locked before the OS
Without the password the drive gives nothing, even when it is taken out of the laptop. The PBA starts from the drive's shadow MBR.
Encryption costs nothing
OPAL drives always encrypt in hardware. The PBA only manages the key, so there is no slowdown and the key never leaves the drive.
Works with what you have
Drives set up with sedutil 1.x keep working: the default hashing is the same, so no passwords have to be set again.
Features
Several drives
Each password is tried on every locked drive; then you can type another password for the rest.
Partitions with their own password
Lock separate partitions with separate passwords, typed one after the other.
SHA-512
PBKDF2-SHA512 with configurable iterations, besides the sedutil-compatible SHA-1.
Hardened image
No service shell, no kernel modules, no network drivers and a locked boot menu.
Current hardware
Linux 6.18 LTS instead of 4.11, and a boot-menu fix for CPUs where the old PBA hangs (sedutil#404).
Reproducible builds
Built in GitHub Actions with published hashes: you can rebuild the image and get the same file.
The same thing others sell per seat — free
Corporate disk-encryption suites use the same OPAL hardware encryption that is built into your SSD. CakesCats PBA unlocks it with open code, at no cost.
| CakesCats PBA | Commercial suites¹ | BitLocker + Intune | |
|---|---|---|---|
| Price | Free, GPL-3.0. Customisation for companies: a flat licence from $3,000 | Per-seat licence or subscription, price on request | Included in Windows Pro and Enterprise; Intune or ConfigMgr licensed separately |
| Drive's hardware encryption | Always: the SSD encrypts, the CPU does nothing | Yes, in OPAL mode | Software by default since 2019 (KB4516071); eDrive must be enabled by policy |
| Source code | Open, reproducible builds with published hashes | Closed | Closed |
| Operating systems | Any OS after unlock: Windows, Linux, dual boot | Depends on the product and its agent | Windows only |
| Pre-boot screen | Fully yours: logo, colours, texts, helpdesk line | Within what the vendor allows | Recovery message and URL |
| SSO and MDM | Entra ID, Okta, Keycloak; Intune, ConfigMgr, Workspace ONE — integrated for your deployment | Through the vendor's management server | Key escrow in Entra ID, policies in Intune |
| Lock-in | None: the open core keeps working without us | Vendor's server and renewals | Microsoft stack |
¹ Trellix (McAfee) Complete Data Protection, WinMagic SecureDoc, Check Point Full Disk Encryption. Dell Encryption Enterprise has been end of sale since 2022. We compare published capabilities; check the details with each vendor.
For companies: as flexible as you need
Your branding, your sign-in, your MDM. One flat licence for the whole fleet instead of paying per seat every year.
Your build, your screen
Logo, background, colours, texts, a helpdesk line and a legal banner. Any setting can be fixed or hidden; extra features can be switched off.
SSO unlock
The PBA shows a QR code, the employee signs in on their phone with Entra ID, Okta, Keycloak or Google Workspace, and your unlock server returns the drive key.
MDM rollout
Enrolment, policies and recovery keys through Intune, ConfigMgr, Workspace ONE or Ivanti; Ansible or Salt for Linux fleets.
Network unlock
On a trusted office network, machines unlock without user input, like BitLocker Network Unlock. Off the network, the password or SSO applies.
Recovery and audit
Recovery passwords in your vault, a log of every unlock, emergency erase, PIN, USB keys and TPM — as your policy requires.
Self-hosted, no cloud of ours
The unlock server runs on your infrastructure. We never see keys or passwords. Secure Boot signing with your own keys.
How it goes
Requirements
A call about your fleet, drives, IdP, MDM and policies.
Pilot
We build your image and test it on your laptop and desktop models.
Rollout
Deployment through your MDM, with a recovery plan and helpdesk instructions.
Updates and support
New kernels and hardware, security fixes and help for your IT team.
You can always check what you run
Corporate builds are made from the same public code as the free image, plus your settings and the integrations you need. They are developed for your deployment, and the scope and timeline go into the contract.
- Source code of your build
- Reproducible images with hashes
- No telemetry
Free, or customised for your company
The open image is free for everyone. Companies buy a licence for customisation, integrations and support — one price for the whole fleet.
The image is free. CakesCats PBA is open source under GPL-3.0: download it, check it, build it yourself. A company licence pays for customisation, integrations and support, and funds the open project.
Guide on GitHubOpen source
The full PBA image and sedutil-cli for anyone, at home or at work.
- Default and hardened images
- Several drives and partitions
- User manual in English and Russian
- Community support on GitHub
Business
Customisation for a company or a team.
- Your skin: logo, colours, texts, helpdesk line
- Settings and features to your policy
- SSO unlock: Entra ID, Okta, Keycloak
- MDM rollout: Intune, ConfigMgr, Workspace ONE
- Secure Boot signing with your keys
- 12 months of updates and support
Enterprise
For a larger fleet with several hardware models.
- Everything in Business
- Pilot on your laptop and desktop models
- Network unlock in the office
- Unlock audit log and recovery in your vault
- Priority support
Over 1,000 machines
Large organisations and custom requirements.
- Everything in Enterprise
- Highly available unlock servers
- Features developed to your requirements
- SLA and on-site help
Prices in USD, excluding taxes. The licence covers the number of machines in your fleet. Questions: mail@cakescats.com
Technical specifications
| Standard | TCG OPAL 2.0 self-encrypting drives, SATA and NVMe |
|---|---|
| Firmware | UEFI, x86_64; boots any OS after unlock |
| Base | Buildroot 2026.02 LTS, Linux 6.18 LTS |
| Image | 32 MiB; default and hardened profiles |
| Password hashing | PBKDF2-SHA1, 75,000 iterations (as in sedutil 1.x) or PBKDF2-SHA512 |
| Tools | sedutil-cli, static build for Linux |
| Tested on | KIOXIA XG8 NVMe, in a VM and on bare metal; more drives in testing |
| Licence | GPL-3.0-or-later, like sedutil |
Frequently asked questions
Is it really free?
Will it work with my drive?
sedutil-cli --scan and test the image from a USB stick first, as the manual describes.What if the password is lost?
How is it different from BitLocker?
What about sleep and hibernation?
Do you get our keys or passwords?
Other CakesCats products
CakesCats is a non-profit project: every product is open source and can be downloaded for free or built yourself from our step-by-step guide. You pay only for hardware, setup and support — and that funds the project.
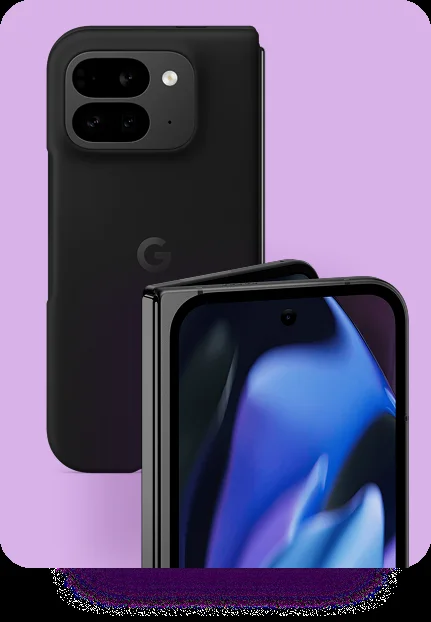
CakesCats Phone
Google Pixel with GrapheneOS, private apps and isolated profiles — configured and ready.
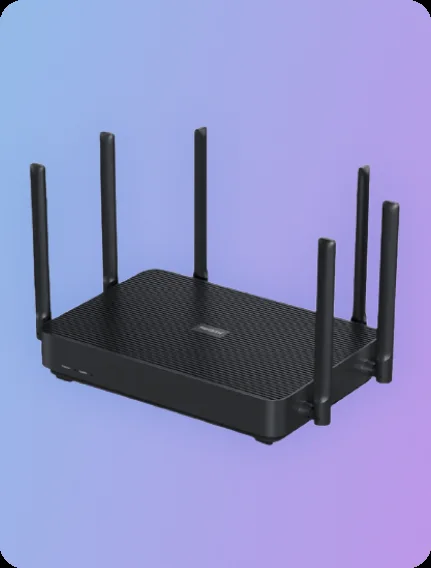
VPN Router
A plug-and-play router with a dedicated V2Ray server and a separate private Wi-Fi network.
VirtualCatsOS
An isolated virtual workspace for Macs with Apple silicon, with encrypted storage and Tor routing.
LLM EdgeBox
A private AI appliance: chat, documents and automation on your premises, with no cloud.
The CakesCats family
All our sites and products.
Encrypt your company's fleet without paying per seat
Tell us about your fleet, IdP and MDM, and we'll propose a pilot.